Skip to content
From MSP to MSSP

Your brand.
Your clients.
Your security offering.

Build your managed security service provider (MSSP) offering with Fig Group. White-label our platform, specialist security testing and certification services, keep the customer relationship and expand without assembling a fragmented tool stack.

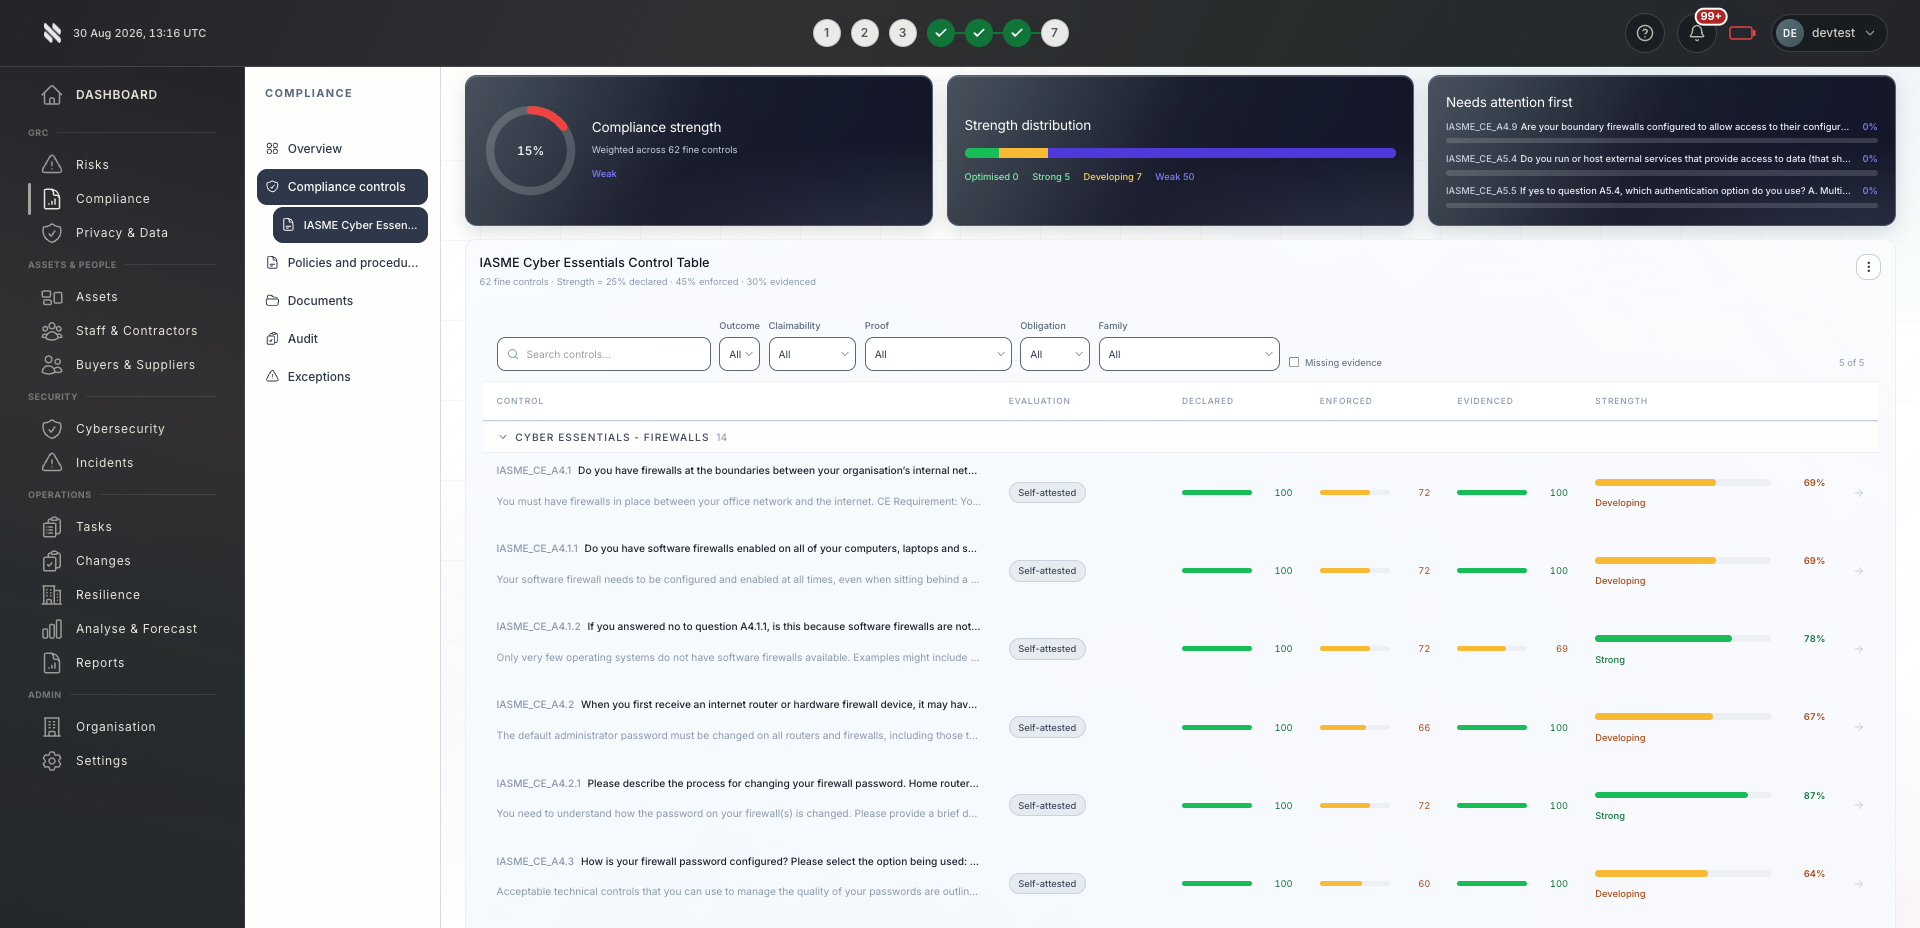
Fig Cyber Essentials control table showing declared, enforced and evidenced control strength
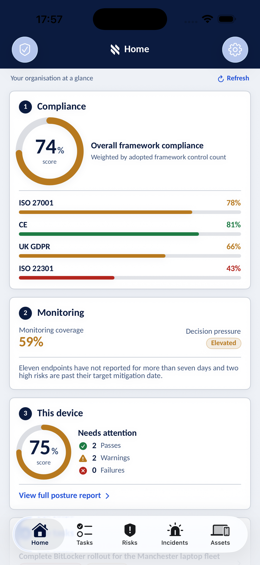
Fig mobile app Home screen showing framework compliance, monitoring coverage and device posture

Key platform statistics

300+
Integrations
48hr
Go-Live
65+
Frameworks
100%
Audit-Ready
From MSP to MSSP

One partner for your whole security service line.

Become a managed security service provider without stitching together separate vendors. Fig Group brings the platform, delivered security services, client certification and insurance-ready evidence into one white-label partnership.

Offer Fig Group’s platform, security testing and certification services under your brand while keeping the client relationship. We agree branding, delivery responsibilities and client communications with you. Certification remains subject to scheme rules: required certification-body details, scheme marks and client declarations are retained.

Connected network equipment in server racks

The compliance and security platform

Deliver compliance automation and cybersecurity as a service from one multi-tenant platform. Monitoring, risk, remediation and evidence for every client, in your branding, with a workspace for each.

Explore the platform
Reviewing documents to identify areas needing attention

White-label security services

Fig Group delivers vulnerability scanning, reviews and penetration testing on your behalf under your brand. You keep the client relationship; we agree scope and permissions together.

Explore security services
Colleagues coordinating work on laptops

Client certification

Offer Cyber Essentials, Cyber Essentials Plus and DCC Level 0 and Level 1 through Fig Compliance Ltd, without becoming a certification body yourself.

How client certification works
A team reviewing documents together at a meeting

Insurance-ready evidence

Help clients bring certification, monitoring and compliance evidence together for conversations with their broker or insurer. Fig Group’s own insurance services are planned, not part of today’s offering.

Explore insurance evidence
End-to-end client management

From the first connection to evidence of progress.

Connect your clients

Agree each client’s scope, connect supported systems and establish the asset inventory and control baseline.

Identify the gaps

Monitor connected security and compliance signals. Add specialist testing where a deeper investigation is needed.

Manage the fixes

Prioritise risks, assign actions and track progress. Your team and client approve and implement changes according to the agreed service scope.

Show the outcome

Report progress to clients, retain evidence and work with Fig Group on certification when the client is ready for assessment.

Connect the full compliance picture for every client:

  • Asset discovery
  • Vulnerability risk
  • Supplier risk
  • Policy management
  • Staff training
  • Remediation
  • Incident records
  • Continuity planning
  • Audit evidence

Monitoring intervals and coverage depend on the connected systems and agreed scope.

How live cybersecurity and compliance monitoring works
Your team and your clients

One platform. Two views. Clear accountability.

Your MSP portfolio view

See client posture, open actions, SLA status and remediation priorities across your portfolio. Assign work and track evidence without rebuilding a separate report for every client.

Your branded client workspace

Give each client visibility of its own posture, the work you are doing and the evidence behind it. Keep your brand and your relationship at the centre of delivery.

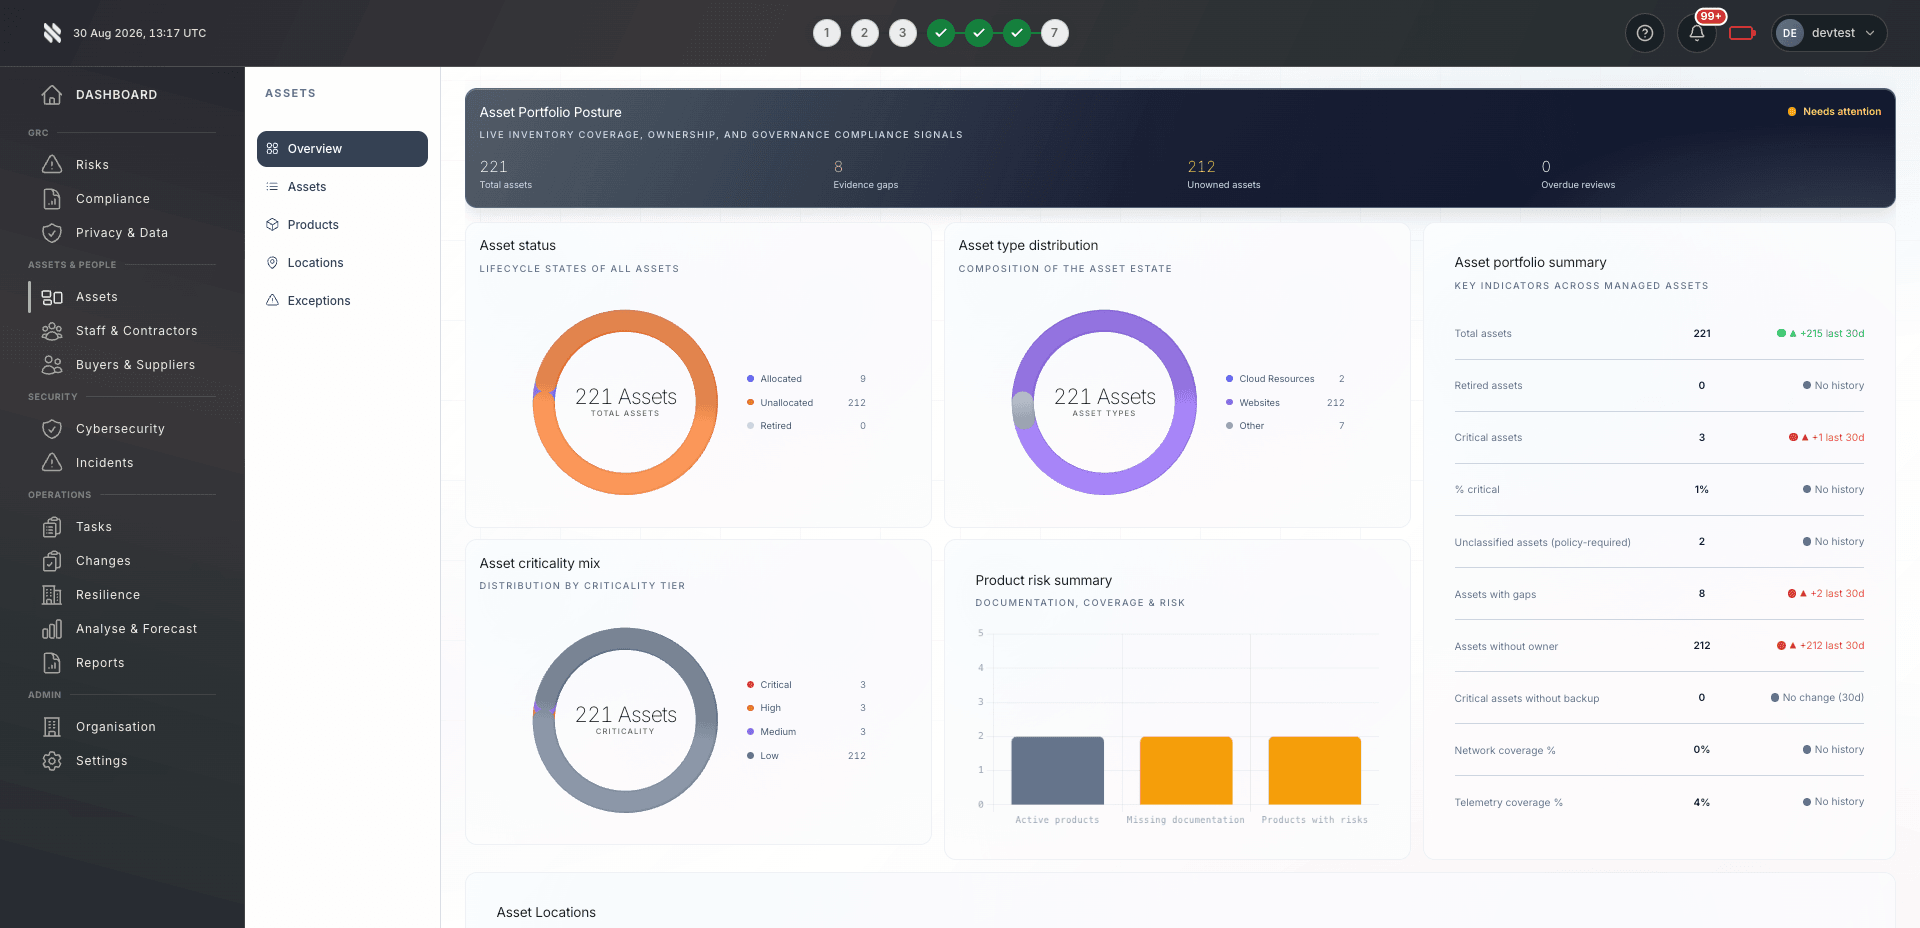
Fig asset portfolio showing inventory coverage, ownership, asset status and criticality
Fig mobile app Home screen showing framework compliance, monitoring coverage and device posture
Specialist security testing

Six services you can offer under your brand.

Bring Fig Group’s testing expertise into your client offering. Agree the scope and permissions, receive actionable findings and coordinate the next steps with your client.

Vulnerability scanning

Automated checks of agreed websites and systems for known weaknesses, helping you prioritise what needs attention.

Explore vulnerability scanning

Device security reviews

Review laptop and mobile-device protection, including encryption, screen locks, updates and lost-device risks.

Explore device security reviews

Cloud security reviews

Review AWS, Azure or Google Cloud configurations, including access permissions, exposed storage, account protection and logging.

Explore cloud security reviews

Public exposure checks (OSINT)

Identify information an attacker can find publicly, such as exposed files, leaked credentials and lookalike domains.

Explore public exposure checks

Code security reviews

Examine source code for weaknesses such as embedded secrets, unsafe input handling and missing access checks.

Explore code security reviews

Penetration testing

A qualified tester attempts to exploit weaknesses in agreed applications, APIs or networks, with written authorisation. Includes a report, fix guidance and a retest of the findings.

Explore penetration testing
Certify your clients with Fig Group

You lead the relationship. We provide the certification assessment.

Offer Cyber Essentials, Cyber Essentials Plus and Defence Cyber Certification Level 0 and Level 1 through Fig Compliance Ltd. You do not need to become a certification body to offer clients a route to certification with us.

Verify our certification licencesCalculate portfolio pricing
Hands working on a laptop at a wooden desk
Cyber Essentials certification body badge

How Cyber Essentials works together

We work with MSPs to certify their clients. Your team can complete the Cyber Essentials self-assessment on the client’s behalf, provided the organisation reviews and authorises the submission and its board-level representative or equivalent provides the required sign-off in the Cyber Essentials portal. Fig Compliance Ltd carries out the certification assessment; the client organisation holds the certificate.

Explore Cyber Essentials certification details

White-labelling does not change who assesses the organisation or remove the client’s declaration. Certification depends on meeting the scheme requirements.

Read the outsourced IT certification guide

IASME guidance on assessment and sign-off

Delivery that fits your team

Choose who does the compliance work.

In every model, you keep the client relationship. Security testing and certification assessments are separately scoped or included in an agreed package.

Reviewing documents at a desk

Managed by Fig Group

Fig Group manages the agreed compliance assessment and evidence-collection work. You maintain the client relationship and coordinate any client-side changes.

Colleagues collaborating around laptops in an office

MSP-led compliance

Your team runs the compliance readiness work. Fig Group’s platform supports monitoring, evidence tracking and reporting. Formal certification is assessed by the licensed certification body.

A team discussing documents around a meeting table

Shared delivery

Split the compliance work between your team and Fig Group. Agree who collects evidence, manages actions and communicates with the client before delivery begins.

Before we start

Agree the scope. Keep control.

We confirm client numbers, integrations, monitoring coverage, hosting, branding and delivery responsibilities before onboarding. Your quote distinguishes the platform, testing and certification services.

Fig Group connects to your existing environment. You do not have to replace your RMM, PSA or endpoint protection simply to use it.

Connected network equipment in server racks

Available today and what comes next

This offering brings together the platform, security testing and certification. A staffed 24/7 security operations centre, incident response retainers and Fig Group’s own insurance capabilities are on the roadmap, not included services.

Continuous monitoring is not automatic certification. An incident-management workflow is not a staffed incident response service.

Partner questions

Know what you can offer.

Practical answers about branding, client certification, monitoring and delivery.

Can we white-label all of Fig Group’s services?

Offer Fig Group’s platform, security testing and certification services under your brand while keeping the client relationship. We agree branding, delivery responsibilities and client communications with you. Certification remains subject to scheme rules: required certification-body details, scheme marks and client declarations are retained.

Can Fig Group work with us to certify our clients?

We work with MSPs to certify their clients. Your team can complete the Cyber Essentials self-assessment on the client’s behalf, provided the organisation reviews and authorises the submission and its board-level representative or equivalent provides the required sign-off in the Cyber Essentials portal. Fig Compliance Ltd carries out the certification assessment; the client organisation holds the certificate.

Do we keep the customer relationship?

Yes. You remain the client’s service partner. We agree how Fig Group supports you, how reports are branded and when assessors or testers need to engage with the client. Required scheme declarations and testing permissions still apply.

Does Fig Group help us become an MSSP without buying fragmented tooling?

Yes. Fig Group brings the platform, specialist security testing and certification services together so you can build a managed security service provider (MSSP) offering through one partner. It connects to your existing environment; it is not a claim to replace every RMM, PSA, endpoint protection or specialist detection tool.

What is monitored, and how often does it update?

Depending on connected systems and agreed scope, monitoring can cover asset inventory, vulnerabilities, configuration and control evidence. Data refresh depends on the integration and check schedule. We confirm supported sources, monitoring intervals and coverage during scoping; not every check is real-time.

Who fixes the issues that monitoring or testing finds?

The agreed owner, usually your team or the client’s technical team, approves and implements changes. Fig Group supports prioritisation, remediation workflows and evidence tracking. Any additional hands-on remediation is separately agreed; a finding does not automatically authorise a change.

Which frameworks and certifications are supported?

The platform supports compliance workflows across frameworks including ISO 27001, SOC 2, Cyber Essentials and DCC. Framework support does not mean Fig Group issues every associated certification. Fig Compliance Ltd delivers Cyber Essentials, Cyber Essentials Plus and DCC Level 0 and Level 1 certification services under the relevant licences.

Are security testing and certification included in the platform price?

They are distinct services. We can agree a combined partner package or scope them separately. Your quote identifies the platform subscription, any testing, certification assessments and delivery responsibilities.

Is a staffed 24/7 SOC, incident response retainer or insurance included?

No. The current offering described here is the platform, security testing and certification services. A staffed 24/7 security operations centre, incident response retainers and Fig Group’s own insurance capabilities are planned services, not included in this offering. Monitoring does not guarantee security or certification.

Can we keep our existing tools?

Yes. Fig Group connects with supported RMM, PSA, cloud, identity and security tools. We confirm the integrations relevant to your clients before onboarding. You can run Fig Group alongside your existing tools during evaluation.

What are the platform contract and support options?

MSP platform packages have an annual contract with monthly or annual payments, no multi-year lock-in, no onboarding fees and no integration surcharges. Give at least 60 days’ written notice before the end of the current annual term to cancel renewal. Cross-customer integrations are included as standard, subject to the required customer permissions. The Master Services Agreement applies alongside your Order Form and MSP terms. Support includes a named onboarding lead, technical support and quarterly business reviews. Confirm scope and the applicable SLAs in your agreement.

Where is client data hosted, and can it be exported?

We confirm the hosting model, data location, access permissions and responsibilities for your deployment before you sign. Clients retain ownership of their data and can export it in standard formats. Your proposal identifies the arrangements that apply to your service.
Become a Fig Group partner

Build your security service line with us.

Tell us about your clients and the services you want to offer. We will show you the platform, explain how we certify clients together and scope the support you need.

Speak to Fig

Tell us what you need. We’ll help you take the next step.

A brief message is all we need to get started.