Manage and monitor
Bring client oversight, security and compliance monitoring, risks, policies, remediation tasks and reporting together on the Fig Group platform.
Explore the platformA finding is useful only when someone can act on it. Fig Group brings the software, specialist services and certification support together so your team can manage the work from the first review to the next assessment.
Use the platform to manage day-to-day activity, bring in specialist testing where you need it, and work with Fig Group for certification. Each service has a clear scope and a direct route to the team delivering it.
Bring client oversight, security and compliance monitoring, risks, policies, remediation tasks and reporting together on the Fig Group platform.
Explore the platformSpecialist vulnerability scanning, device and cloud reviews, public exposure checks, code reviews and penetration testing, with findings your team can act on.
Explore security testingCyber Essentials, Cyber Essentials Plus and Defence Cyber Certification Level 0 and Level 1, delivered through Fig Compliance Ltd.
Explore certificationBring the discussion back to the assets, findings and dependencies behind a priority, with a shared view for the people responsible.
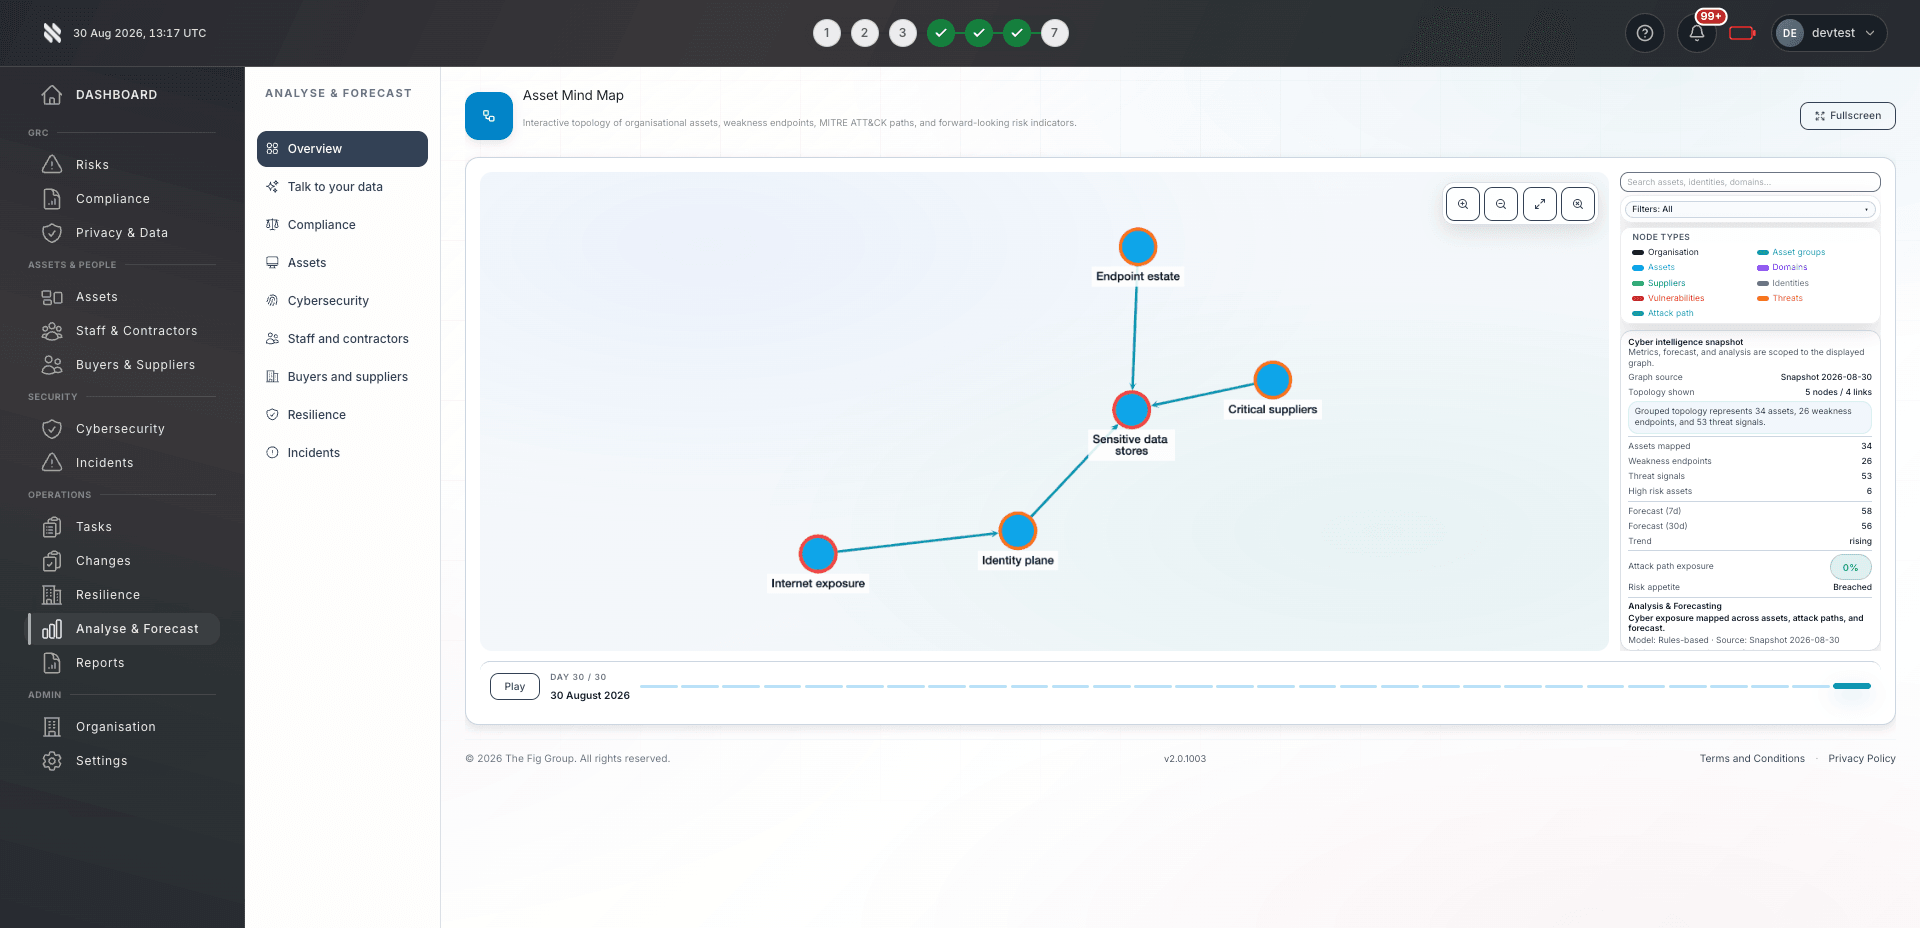
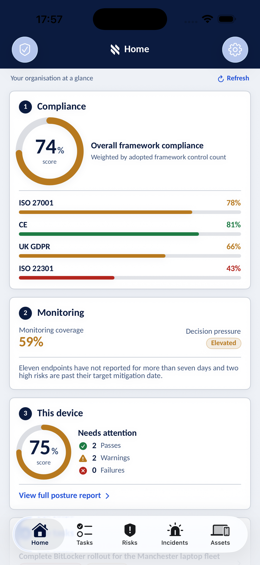
Connect governance to IT service management (ITSM): the operational work of assigning, approving and resolving tasks. Policies and commitments from a due diligence questionnaire (DDQ) should inform that work, not sit in a separate document.
Start with your clients, internal policies, contractual commitments and certification requirements. Confirm the platform capabilities, integrations and specialist services needed for that scope.
Bring findings, policies and evidence into the relevant workflows. Define owners, review points and approvals so the team can see what needs to happen next.
Track actions and retain evidence of the outcome. Use that record in client reviews, internal oversight and assessment preparation, with open issues still visible.
For MSPs and their clients
Offer Fig Group’s platform, security testing and certification services under your brand while keeping the client relationship. We agree branding, delivery responsibilities and client communications with you. Certification remains subject to scheme rules: required certification-body details, scheme marks and client declarations are retained.
Internal teams can also work directly with Fig Group, or share oversight with their existing MSP. Agree responsibilities, permissions and reporting before delivery begins.
The right choice depends on your requirements. Ask to see the relevant workflows and confirm what is included before deciding.
Which client activities can move into the platform, what systems remain, and how will data move between them?
Plan tool consolidationWho reviews findings, approves actions and delivers testing? Which certification assessment is required, and what remains the client’s responsibility?
Review specialist servicesReview our certification credentials, published pricing and guarantee terms. Platform access is not a certificate or a guarantee that security incidents cannot occur.
Read our claim evidenceWhat is included, what stays with your team and how to get started.
Fig Group combines a cybersecurity and compliance platform with specialist security testing and compliance certification services. You can use the relevant services for your organisation or deliver them to clients through an MSP partnership.
No. Start by reviewing your required workflows and integrations with Fig Group. Some work can be consolidated in the platform, while specialist or operational systems may remain in place. Agree coverage before changing your stack.
No. Automation helps teams monitor requirements, assign work and retain evidence. People still need to configure the service, review findings and decisions, and complete outstanding work. Certification requires its own assessment.
Offer Fig Group’s platform, security testing and certification services under your brand while keeping the client relationship. We agree branding, delivery responsibilities and client communications with you. Certification remains subject to scheme rules: required certification-body details, scheme marks and client declarations are retained.
The timeline depends on the agreed scope, integrations, data and access arrangements. We confirm the onboarding plan with you before delivery; platform setup and certification assessment are separate activities.
Tell us what you need to manage and the services you want to deliver. We will walk through the relevant platform workflows and delivery options.
| Capability | Fig Group | A disconnected approach |
|---|---|---|
| What it is | Security and compliance platform with separately scoped specialist services | Separate tools and evidence repositories |
| Compliance approach | Connect policies, controls, evidence and responsible owners | Reconcile policy documents and checklists manually |
| Integration model | Connect supported tools to findings and follow-up work | Move evidence between tools and reports |
| Policy management | Draft, approve, distribute and track policy acknowledgement | Maintain versions and acknowledgements separately |
| MSP and client alignment | Agree access, responsibilities and client workflows | Reconcile separate client and provider records |
| Event handling | Route relevant findings into assigned remediation workflows | Review alerts and create follow-up tasks manually |
| Responsibility tracking | Record owners, deadlines and evidence of completion | Track ownership across spreadsheets and messages |
| Data model | Connect client, asset, control and risk records in the agreed scope | Combine separate inventories and reports |
| Gap management | Make unresolved findings and evidence gaps visible for follow-up | Find gaps when separate records are reconciled |
The comparison describes two operating approaches, not a claim that every competing platform lacks these capabilities. Features and integrations depend on the selected Fig package; no platform guarantees that gaps cannot occur.