Understand your exposure
Bring assets, security findings and supplier dependencies into a shared view. See where attention is needed and who is responsible for the next step.
Asset visibilityBring your security findings, compliance evidence and remediation work together. Fig gives your organisation and its MSP a common place to manage the work, with specialist testing and certification available when you need them.
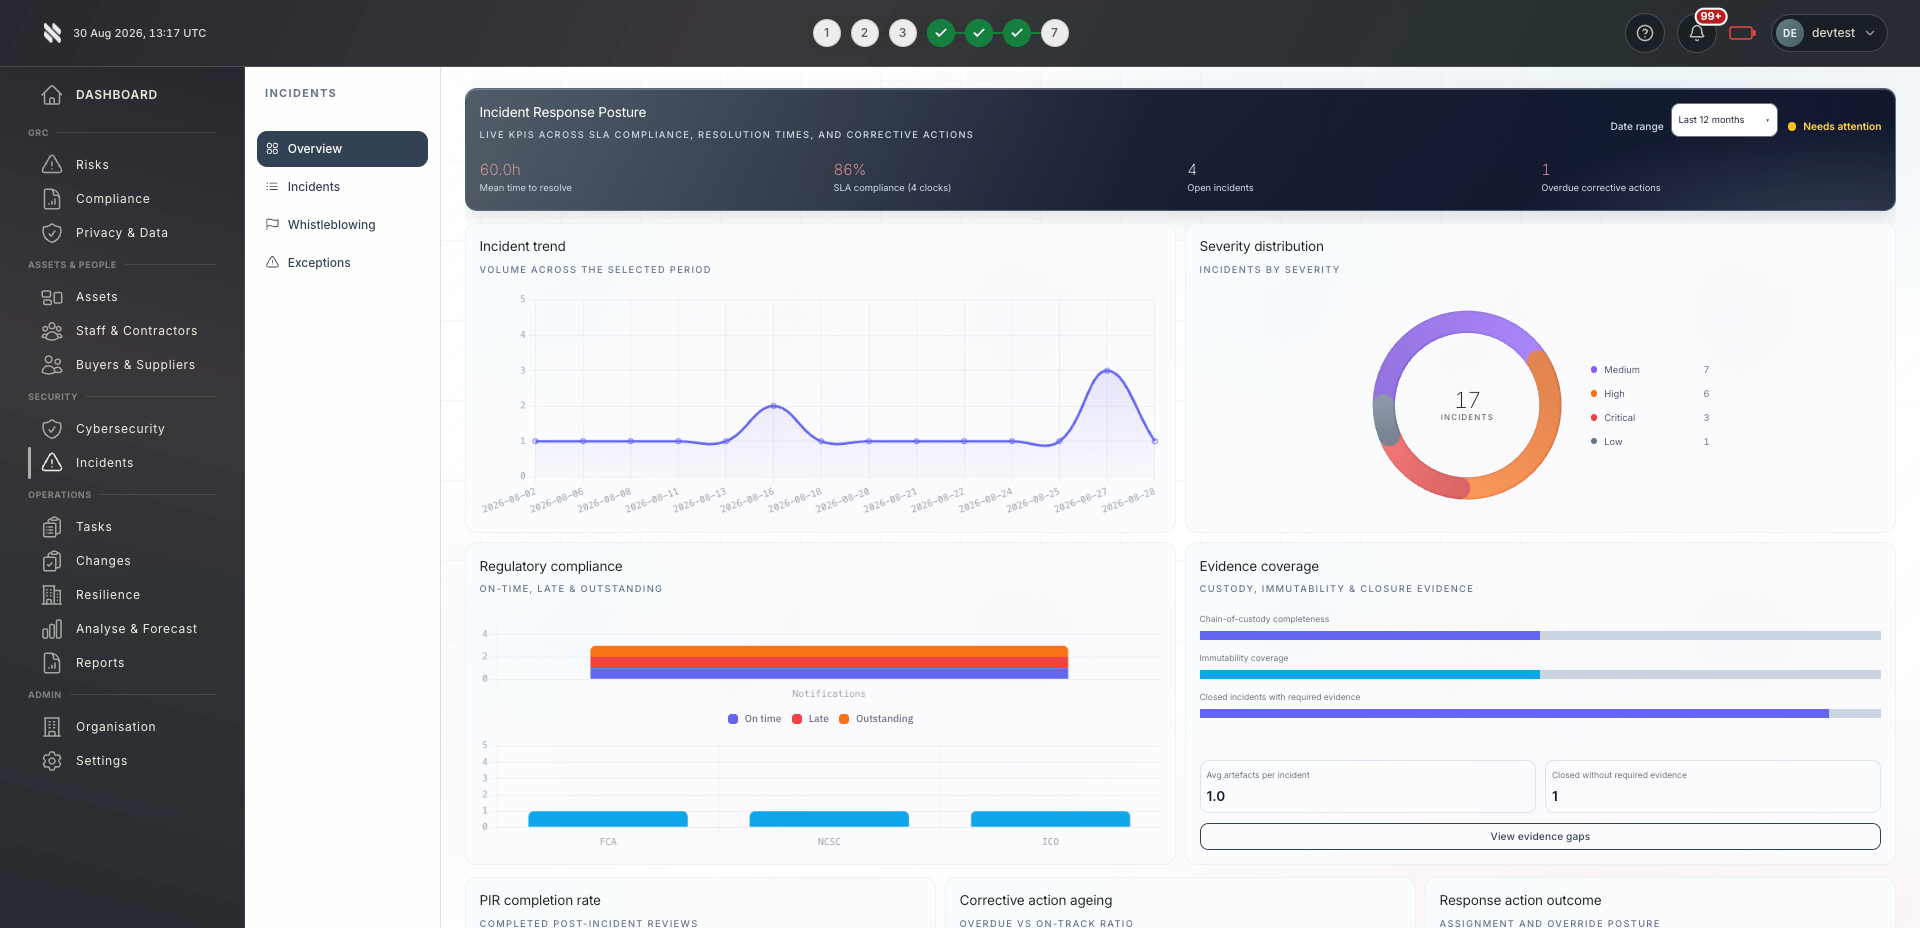
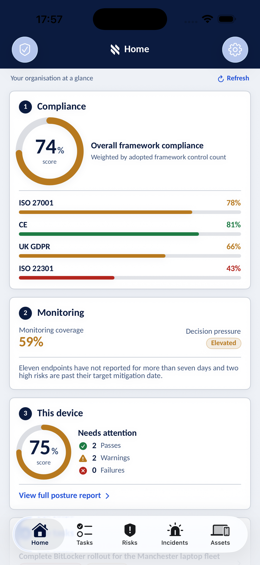
Your security tools, internal policies and external requirements should inform the same set of priorities. Fig connects that information to practical tasks and accountable owners.
Bring assets, security findings and supplier dependencies into a shared view. See where attention is needed and who is responsible for the next step.
Asset visibility
Connect policies, controls, evidence and review tasks. Give your internal team and your MSP a common record of what has been completed and what remains open.
Compliance management
Assign findings to an owner, agree priorities and track progress. Keep approvals and supporting evidence alongside the work, so the outcome can be reviewed.
Remediation workflowsUse the platform to explore critical dependencies and discuss priorities with the teams responsible for them.
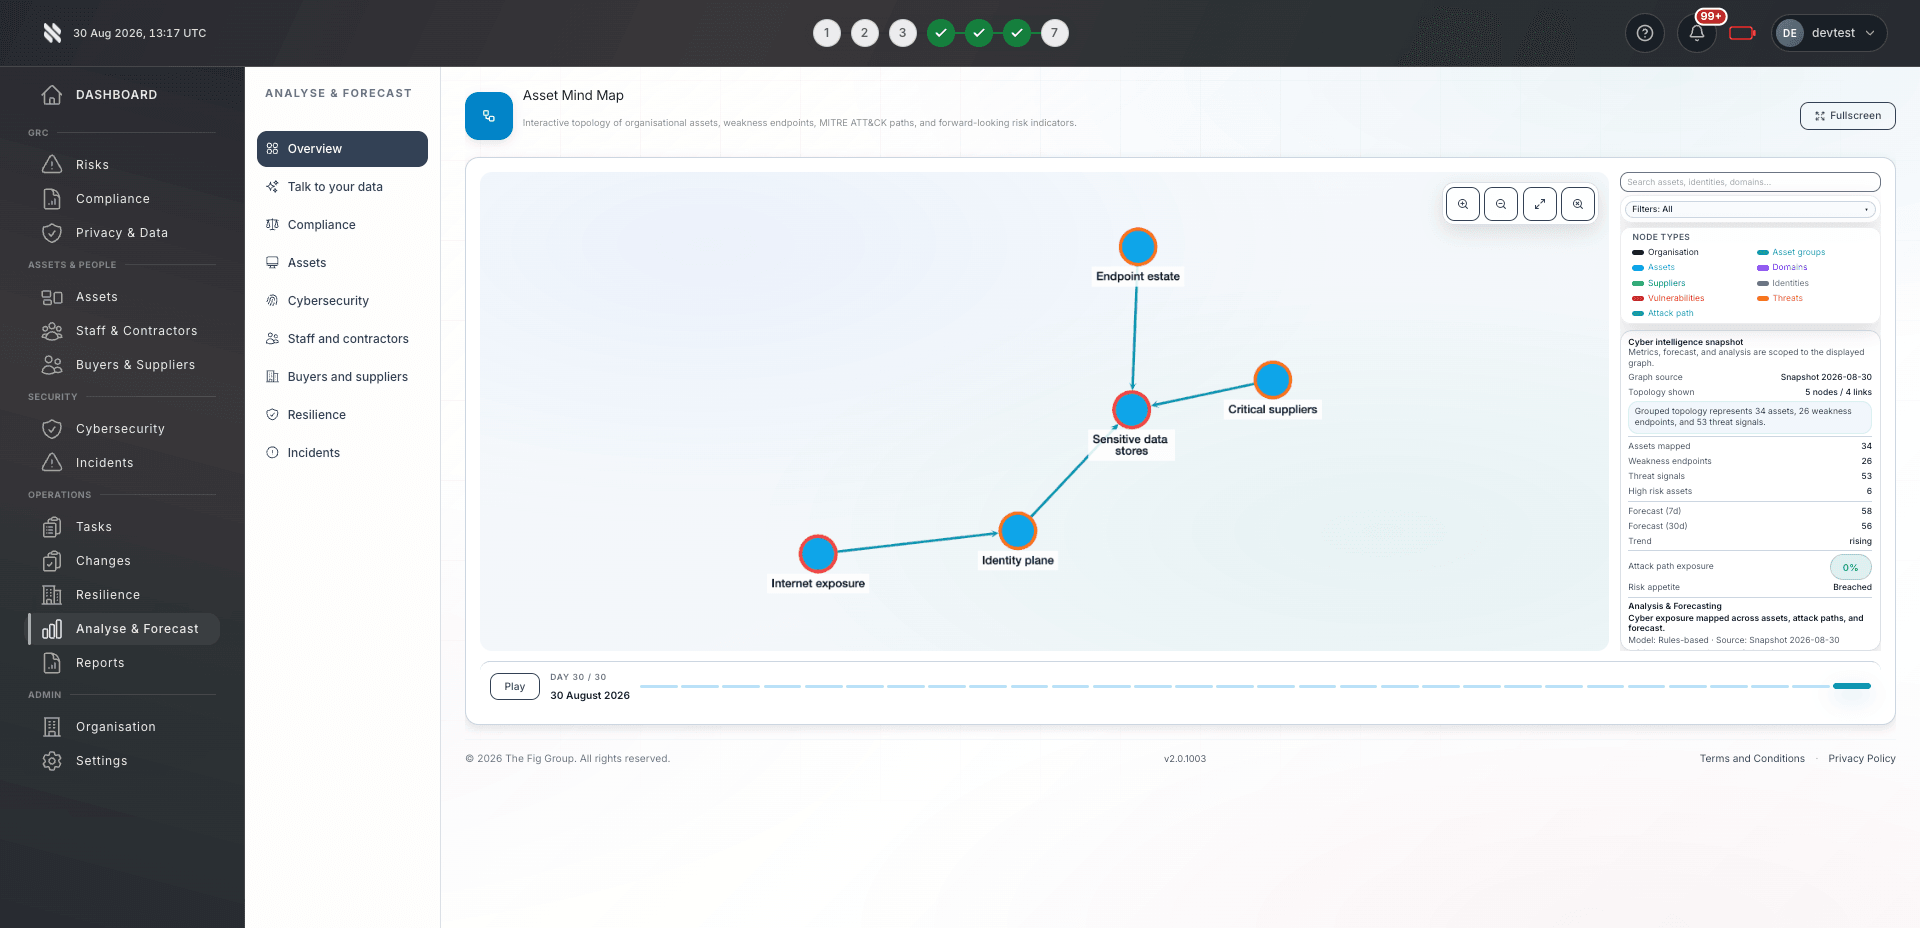
Fig platform · Asset mind map
Your MSP can run the operational work while your team reviews priorities, progress and evidence. Agree who owns each task and keep the record in one place.
If your MSP wants to expand its service, Fig provides the platform, white-label security services and a partnership route to certify clients.
How the MSP partnership worksStart with the work you need to complete. We will agree the platform scope and any specialist engagements around it.
Manage assets, policies, risks, evidence and remediation workflows. Confirm your framework and integration requirements with our team.
Commission vulnerability scanning, device and cloud reviews, code reviews or penetration testing against an agreed scope.
Work with Fig for Cyber Essentials, Cyber Essentials Plus or Defence Cyber Certification. Each service has its own scope and assessment requirements.
How Fig fits with your team, your MSP and the tools you already use.
Yes. Your MSP can manage day-to-day work in Fig while your team retains oversight. We agree access, responsibilities and reporting with you during onboarding.
Not necessarily. We review your systems and integration requirements before agreeing the deployment. Fig brings security and compliance work together; it is not a replacement for every operational tool your team uses.
No. The platform helps you manage controls and evidence. Cyber Essentials, Cyber Essentials Plus and Defence Cyber Certification each require their own assessment. Fig can provide the relevant certification service as a separate engagement.
Yes. Fig offers vulnerability scanning and specialist security testing, including penetration testing. Scope, permissions, deliverables and retest arrangements are agreed before work begins.
Tell us about your organisation, existing systems and priorities. We will discuss the appropriate platform scope, any testing or certification you need, and the onboarding arrangements.
Share your priorities, current systems and any testing or certification deadlines. We will discuss the right next step with you.
Compare Cyber Essentials and Defence Cyber Certification services, with published pricing and clear assessment scopes.