Control Evaluation Engine
Configured evaluators assess connected control evidence against selected framework requirements and internal policies. Coverage and cadence depend on the evaluator, connected source and selected package.
Map controls to frameworks, collect evidence continuously and expose gaps while there is still time to act.
Compliance evidence is assembled once per audit. Framework mapping is inconsistent. New regulations hit without warning. Manual control assessment breaks teams under scale.
Configured evaluators assess connected control evidence against selected framework requirements and internal policies. Coverage and cadence depend on the evaluator, connected source and selected package.
Fig Group can record and review AI-assisted code, configuration and control changes within configured workflows. Connect the source tools and approval gates you intend to govern; unconnected changes are outside that evidence trail.
Evidence collected in real-time from scanners, logs, tickets, and assessments. Audit-ready reports generated on demand, not assembled three weeks before assessment day. Statement of Applicability (SoA) generated automatically for ISMS frameworks.
Live compliance posture across all frameworks. Regulatory reporting timelines tracked automatically with deadline alerts. Gap identification prioritised by audit risk and implementation effort. Audit readiness scoring refreshes weekly.
Fig Group connects control evaluation, evidence and follow-up work across your compliance programme. Start with a defined scope and a real control: see what the connected evidence establishes, who reviews the result and how a gap becomes an owned action.
Connected evidence collection, control evaluation and status reporting can reduce repeated administration. Your team still defines scope, checks whether evidence is sufficient, approves policies and accepts residual risk. Confirm the available evaluators and connections for your proposed deployment; a dashboard result does not itself grant certification.
Fig Group links evidence and control work to framework requirements. Reuse a record where its scope, date and content support each requirement, then review the mapping. A shared document does not mean every requirement is satisfied: retain framework-specific gaps and the reviewer’s reasoning.
Bring your framework list, organisation or client boundaries, current control owners, evidence sources and one recent audit gap. Ask to see an evidence record, its evaluation, a failed or incomplete result, the resulting action and the export a reviewer would receive. Confirm package scope and connector permissions in the quote.
A fictional access review finds a leaver still listed in a source system. The reviewer checks the account and scope, assigns corrective work and records fresh evidence after access is removed. The same evidence may support several mapped requirements, but each control conclusion still needs review.
Ask to follow the source record through evaluation, owner assignment and audit output, including what happens when the source stops updating.
Discuss this workflow with FigExplore the compliance controls view within the Fig platform.
A tailored walkthrough lets you review the relevant workflows, supported connections and reporting before deciding whether Fig is right for your team.
See it in a demo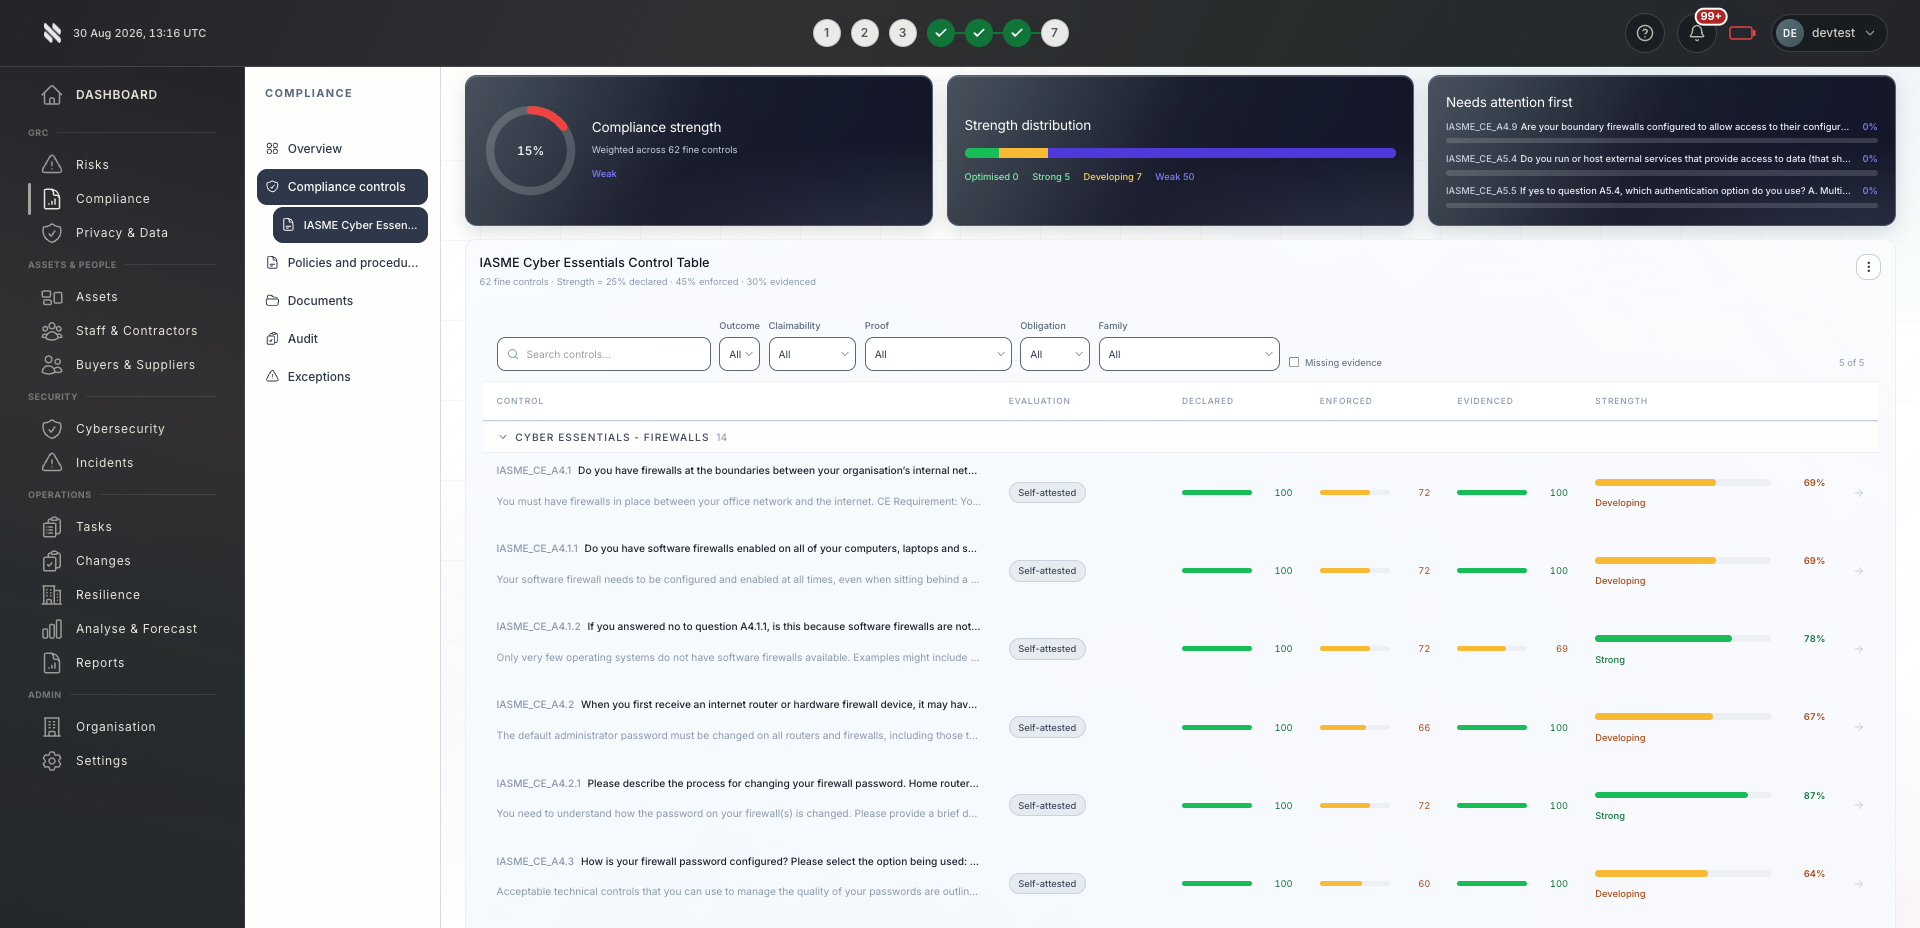
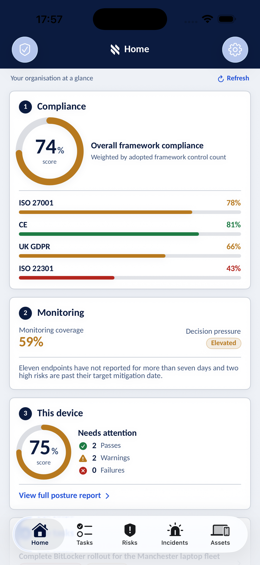
Bring delivery, oversight and assurance together without losing sight of who owns the next action.
Standardised compliance delivery across all client frameworks. White-label compliance reporting and audit readiness tracking strengthens your MSP competitive position.
Explore Fig for MSPs
Integrated compliance across teams - security, audit, operations all contributing evidence to a single framework map. Regulatory change notifications trigger immediate gap identification.
Explore Fig for organisationsPre-built evidence packs linked to every framework control. Historical compliance trends and remediation evidence available for comparatives across audit years.
Discuss your requirementsStart with the outcomes you need. We will discuss scope, delivery and commercial terms with you before you commit.
Choose one framework and a representative business unit or client. Agree control ownership, the evidence period and who can approve exceptions.
Connect the agreed sources, inspect missing or stale records and review a sample of control mappings with your compliance owner.
Take a gap through assignment, treatment and review. Check the exported evidence before extending the rollout to more frameworks or clients.
Platform functionality and automation depend on the agreed scope, configuration and connected systems. Software supports your compliance programme; it does not replace an independent assessment or guarantee certification.
Need to discuss a specific requirement or client scenario?
Speak to FigThe platform catalogue covers 65+ frameworks, including CMMC, DORA, NIS2, ISO 27001, SOC 2, GDPR and Cyber Essentials. Confirm the edition, control mapping and package available for your selected framework; custom mappings need review.
Yes, where the code or configuration enters a connected, configured review workflow. Record its source, version, control checks and human approval before deployment; an AI output alone is not evidence of compliance.
The platform catalogue describes 300+ integrations. Collection depends on the connections enabled, permissions and source refresh schedules. Review missing evidence and control mappings; manual evidence or approval may still be required.
New or revised mappings can be reviewed against your existing controls. The responsible team still determines applicability, validates changed requirements and checks whether existing evidence is sufficient.
Yes. MSPs can give clients access to a live compliance dashboard showing their framework coverage, outstanding gaps, and evidence collection status. Dashboards are white-labelled and role-restricted so clients only see what is relevant to them.
Choose compliance automation by testing the work your team needs to complete: collecting evidence, assigning gaps, reviewing decisions and exporting an auditable record. Use this checklist to compare demonstrated results, not feature counts.
Use the guide and templateTell us what you would like to achieve. We will arrange a relevant conversation about the platform, your requirements and the right next step.
Continue exploring the prove capabilities, or return to the full platform overview.