Skip to content
Fig platform · prove

Policy ManagementConnected to the bigger picture.

Connect policies to owners, approvals, exceptions, attestations and the controls they are supposed to govern.

Professional reviewing business documents
What this means for your team
  • Manage reviews and approvals.
  • Track staff acknowledgement.
  • Link policy obligations to evidence and tasks.
The practical difference

Turn policies into operational control, not static documents.

Policies age without review. Staff never see them. Attestation is manual and incomplete. Policy drift goes undetected. Compliance officers spend weeks on administrative work instead of governance.

01

Policy Lifecycle

60+ pre-built templates covering access control, network security, encryption, supplier management, HR, incident response, and more. Automated workflows from drafting through review, approval, publication, and archival. Version control and change tracking built-in. Approval chains for team leads and managers are mandatory.

02

AI-Assisted Drafting

AI tools can generate policy text, procedures, and control workflows. Fig Group manages versioning, review cycles, and compliance alignment so human teams focus on governance, not formatting.

03

Distribution Tracking

Policies pushed to staff automatically across email, portals, and mobile apps. Read receipts and attestation tracked by individual and role. Non-attesters are escalated automatically. Policy exception and waiver workflows with approval chains and automatic expiration.

04

Compliance Proof

Audit-ready evidence showing which staff read which policies, when, and whether they attested understanding. Policy effectiveness linked to incident and compliance trends.
Inside Fig

See the work.
Keep the evidence.

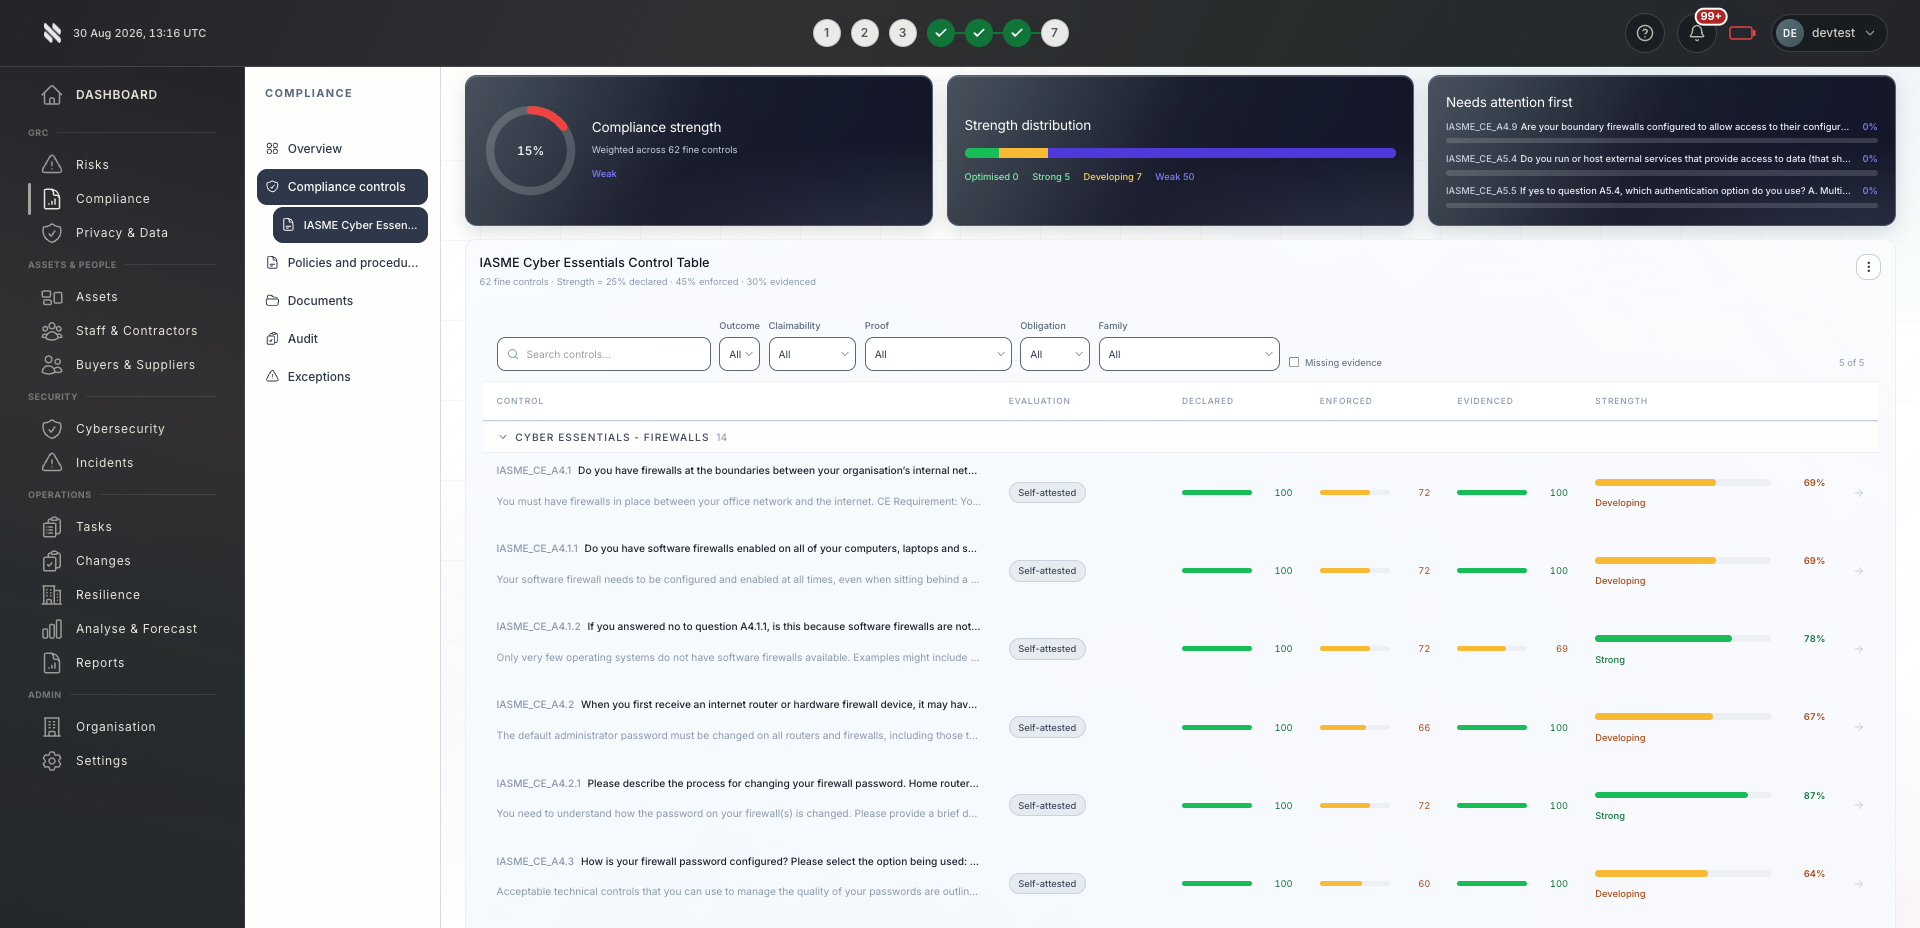
This compliance controls view shows the wider Fig environment. Ask us to demonstrate policy management against your own requirements.

A tailored walkthrough lets you review the relevant workflows, supported connections and reporting before deciding whether Fig is right for your team.

See it in a demo
Fig Cyber Essentials control table showing declared, enforced and evidenced control strength
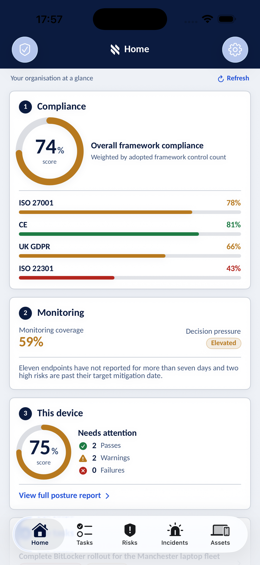
Fig mobile app Home screen showing framework compliance, monitoring coverage and device posture
Fig platform · Compliance controls
Built around your role

One platform. Different responsibilities.

Bring delivery, oversight and assurance together without losing sight of who owns the next action.

Colleagues working together with laptops in an office

MSPs & MSSPs

Standardised policy templates and distribution workflows for all clients. White-label policy management reduces your policy administration overhead while strengthening compliance delivery.

Explore Fig for MSPs
Business team discussing shared priorities

In-house teams

Central policy governance with department-specific variants. Attestation tracking across thousands of staff integrated with onboarding and training systems.

Explore Fig for organisations
Reviewing business records and supporting documentation

Compliance & audit teams

Policy read receipts, attestation records, and change history provide evidence of policy awareness and control over the policy lifecycle.

Discuss your requirements
A considered start

Evaluate the fit. Then agree the rollout.

Start with the outcomes you need. We will discuss scope, delivery and commercial terms with you before you commit.

  1. 1

    Tell us what matters

    Discuss your current approach to policy management, the teams involved and the requirements you need to meet.

  2. 2

    Review the workflows

    See the relevant features in a tailored demonstration. Confirm integration coverage, responsibilities and any configuration needed.

  3. 3

    Agree your next step

    Review the proposed scope and pricing. Set implementation priorities, ownership and review points around your organisation or client portfolio.

Platform functionality and automation depend on the agreed scope, configuration and connected systems. Software supports your compliance programme; it does not replace an independent assessment or guarantee certification.

Before you decide

Your questions, answered.

Need to discuss a specific requirement or client scenario?

Speak to Fig
Can we enforce different policies per department?

Yes. Policies can be targeted by department, role, or clearance level. Variant versions are managed as a single policy unit with centralised change control.

What happens if someone doesn't attest?

Fig Group tracks non-attestation and escalates automatically to line managers and compliance officers. Escalation timelines and notification templates are fully configurable.

Can we use our existing policies?

Yes. Bring your existing policies so we can confirm supported file formats and any conversion or review needed. Fig Group adds version control, distribution tracking and attestation workflows. Approve the imported version before distribution; an acknowledgement records receipt, not proof of understanding.

How do we know which policies are out of date?

Fig Group tracks review dates for every policy and flags upcoming and overdue reviews on your dashboard. You set the review cycle per policy, whether that is quarterly, annually, or tied to regulatory changes. Overdue policies are escalated to the assigned owner automatically.

Can we roll out the same policy templates across all our MSP clients?

Yes. Create a master policy template once, then distribute it across client tenants. Each client can have localised variations where needed, but the core template stays centrally managed so updates propagate consistently.

Take the next step

See how policy management could work for you.

Tell us what you would like to achieve. We will arrange a relevant conversation about the platform, your requirements and the right next step.

  • A walkthrough focused on your priorities
  • Clarity on scope, connections and delivery
  • A discussion of pricing for your requirements

Speak to Fig

Tell us what you need. We’ll help you take the next step.

A brief message is all we need to get started.