ROPA and Data Mapping
Maintain controller and processor processing records with fields relevant to Article 30, including purpose, lawful basis, retention and transfers. Review completeness and applicability with the responsible privacy team.
ROPA, DPIA, DSAR, consent management, breach notification, and Privacy by Design.
Privacy compliance lives in spreadsheets and shared drives. DSAR responses miss statutory deadlines. Processing activities are undocumented. Breach notifications are assembled under pressure with incomplete data.
Maintain controller and processor processing records with fields relevant to Article 30, including purpose, lawful basis, retention and transfers. Review completeness and applicability with the responsible privacy team.
Structured DPIA screening and assessment linked to change management. Track subject access requests, applicable timelines, review, redaction and response decisions.
Track consent where it is the lawful basis, alongside other lawful bases and processing records. Breach workflows support risk assessment and notification timing after awareness; a human decides whether notification is required.
Project-level privacy assessments for new systems and changes. Data deletion and portability controllers. Legal hold management with retention exceptions. Personal data inventory linked to the asset register.
This compliance controls view shows the wider Fig environment. Ask us to demonstrate privacy & data protection against your own requirements.
A tailored walkthrough lets you review the relevant workflows, supported connections and reporting before deciding whether Fig is right for your team.
See it in a demo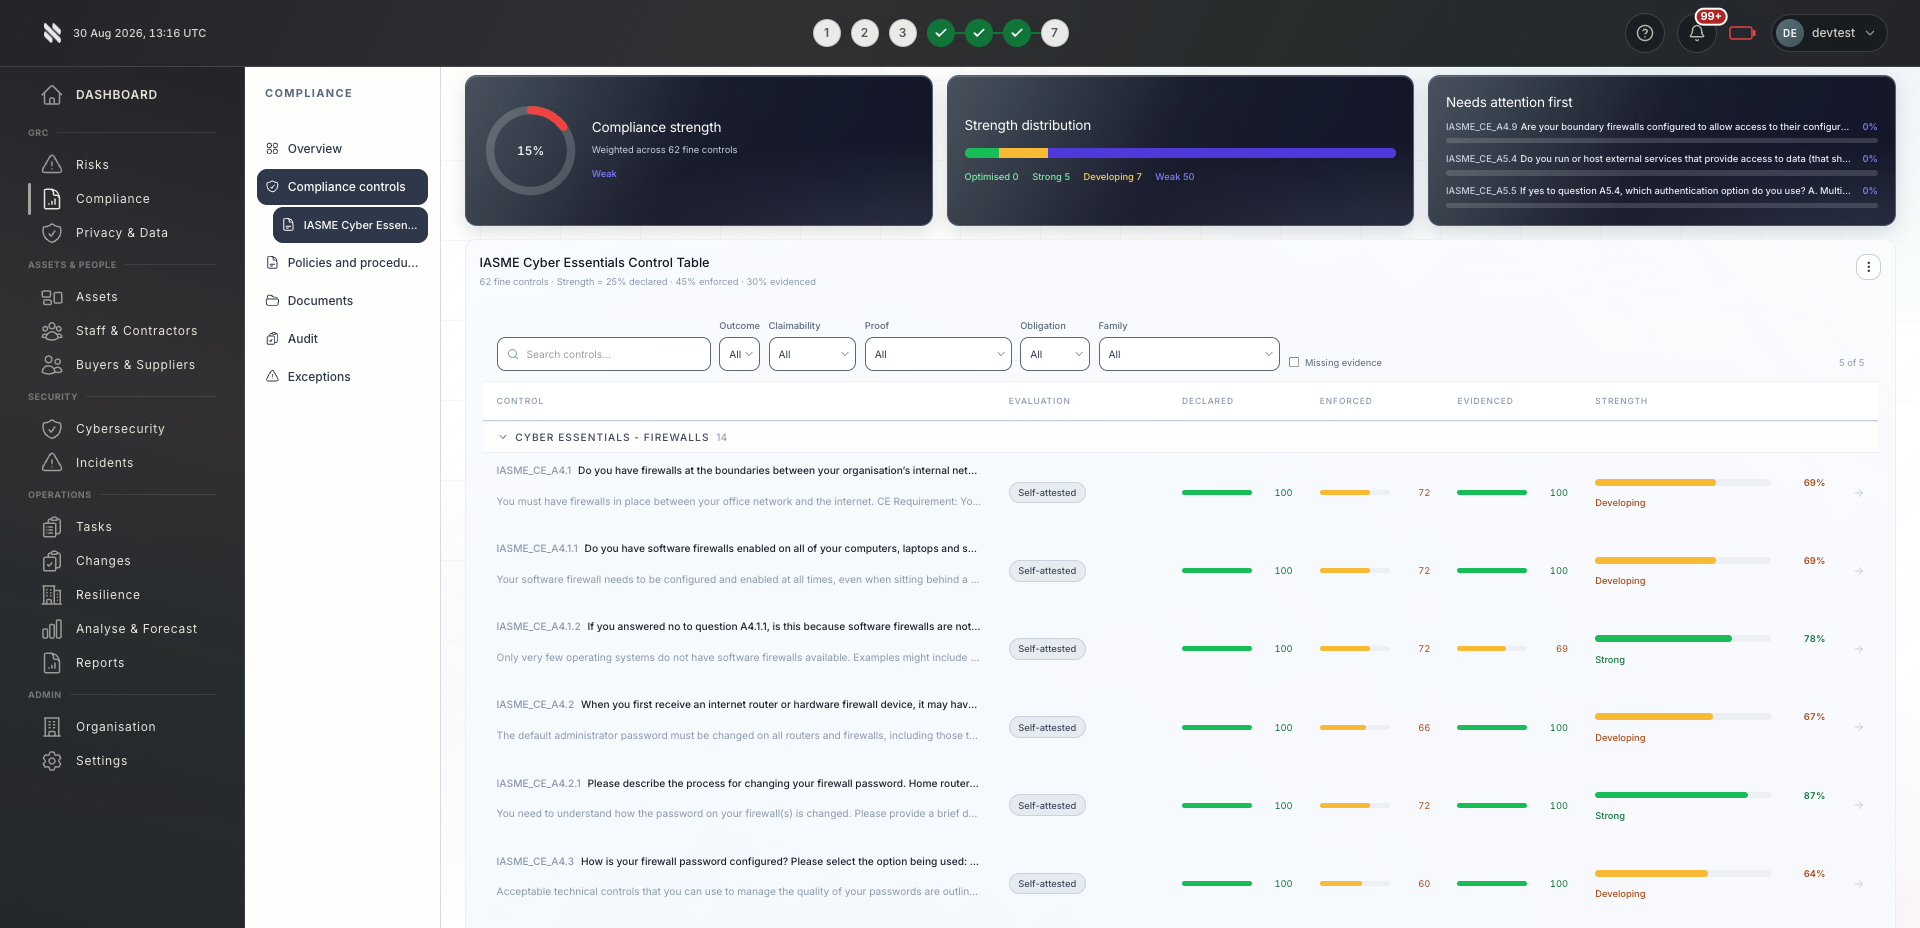
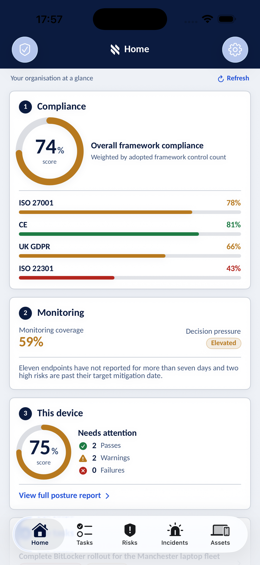
Bring delivery, oversight and assurance together without losing sight of who owns the next action.
Deliver privacy compliance as a managed service. Multi-tenant ROPA, DSAR management, and breach notification across client portfolios.
Explore Fig for MSPs
Connect privacy, supplier and incident records. For a personal-data breach, assess the affected processing population across relevant systems and lawful bases, then record the awareness time, risk assessment and notification decision.
Explore Fig for organisationsComplete evidence chain from processing activity registers through impact assessments, consent records, breach notifications, and deletion logs for GDPR, UK GDPR, and DORA compliance.
Discuss your requirementsStart with the outcomes you need. We will discuss scope, delivery and commercial terms with you before you commit.
Discuss your current approach to privacy & data protection, the teams involved and the requirements you need to meet.
See the relevant features in a tailored demonstration. Confirm integration coverage, responsibilities and any configuration needed.
Review the proposed scope and pricing. Set implementation priorities, ownership and review points around your organisation or client portfolio.
Platform functionality and automation depend on the agreed scope, configuration and connected systems. Software supports your compliance programme; it does not replace an independent assessment or guarantee certification.
Need to discuss a specific requirement or client scenario?
Speak to FigCompare the ROPA, DPIA, DSAR, consent, cookie, vendor and breach workflows you actually use, including integrations and package scope. Fig Group may cover selected privacy governance needs or work alongside a specialist service.
Record when the organisation became aware of a suspected personal-data breach, link the affected processing activities and investigate people affected across all relevant sources, including processing that does not rely on consent. A responsible reviewer assesses risk, jurisdiction and exemptions, then decides whether and when to notify.
Yes. Subject access requests are tracked from intake through to response with statutory deadline monitoring. Response workflows include data gathering, review, redaction, and delivery with full audit trails.
A flagged change can trigger privacy screening before approval. A qualified reviewer decides whether the proposed processing is likely to be high risk and needs a DPIA, then records the assessment and any required actions.
Yes. Fig Group supports both UK GDPR and EU GDPR requirements, including the differences in supervisory authority notification, data transfer mechanisms, and lawful basis documentation.
Tell us what you would like to achieve. We will arrange a relevant conversation about the platform, your requirements and the right next step.
Continue exploring the prove capabilities, or return to the full platform overview.