QMS Framework
ISO 9001:2015 clause applicability mapping with scope definition, interested parties register, and process documentation. Quality objectives tracked alongside security controls.
ISO 9001 QMS with CAPA, process mapping, internal audits, and management review.
Quality management lives in a separate system from information security. ISO 9001 and ISO 27001 audits run independently with duplicated evidence collection. CAPA processes are manual and findings go untracked.
ISO 9001:2015 clause applicability mapping with scope definition, interested parties register, and process documentation. Quality objectives tracked alongside security controls.
Corrective and Preventive Actions with root cause analysis, corrective action tracking, effectiveness review, and closure verification. Linked to audit findings and incident outcomes.
QMS audit scheduling, execution, and findings management using the same audit infrastructure as ISO 27001 assessments. One audit engine for both quality and security.
Structured management review with inputs from audits, CAPA, customer feedback, process metrics, and KPIs. Output actions tracked through to completion with board-ready reporting.
This compliance controls view shows the wider Fig environment. Ask us to demonstrate quality management against your own requirements.
A tailored walkthrough lets you review the relevant workflows, supported connections and reporting before deciding whether Fig is right for your team.
See it in a demo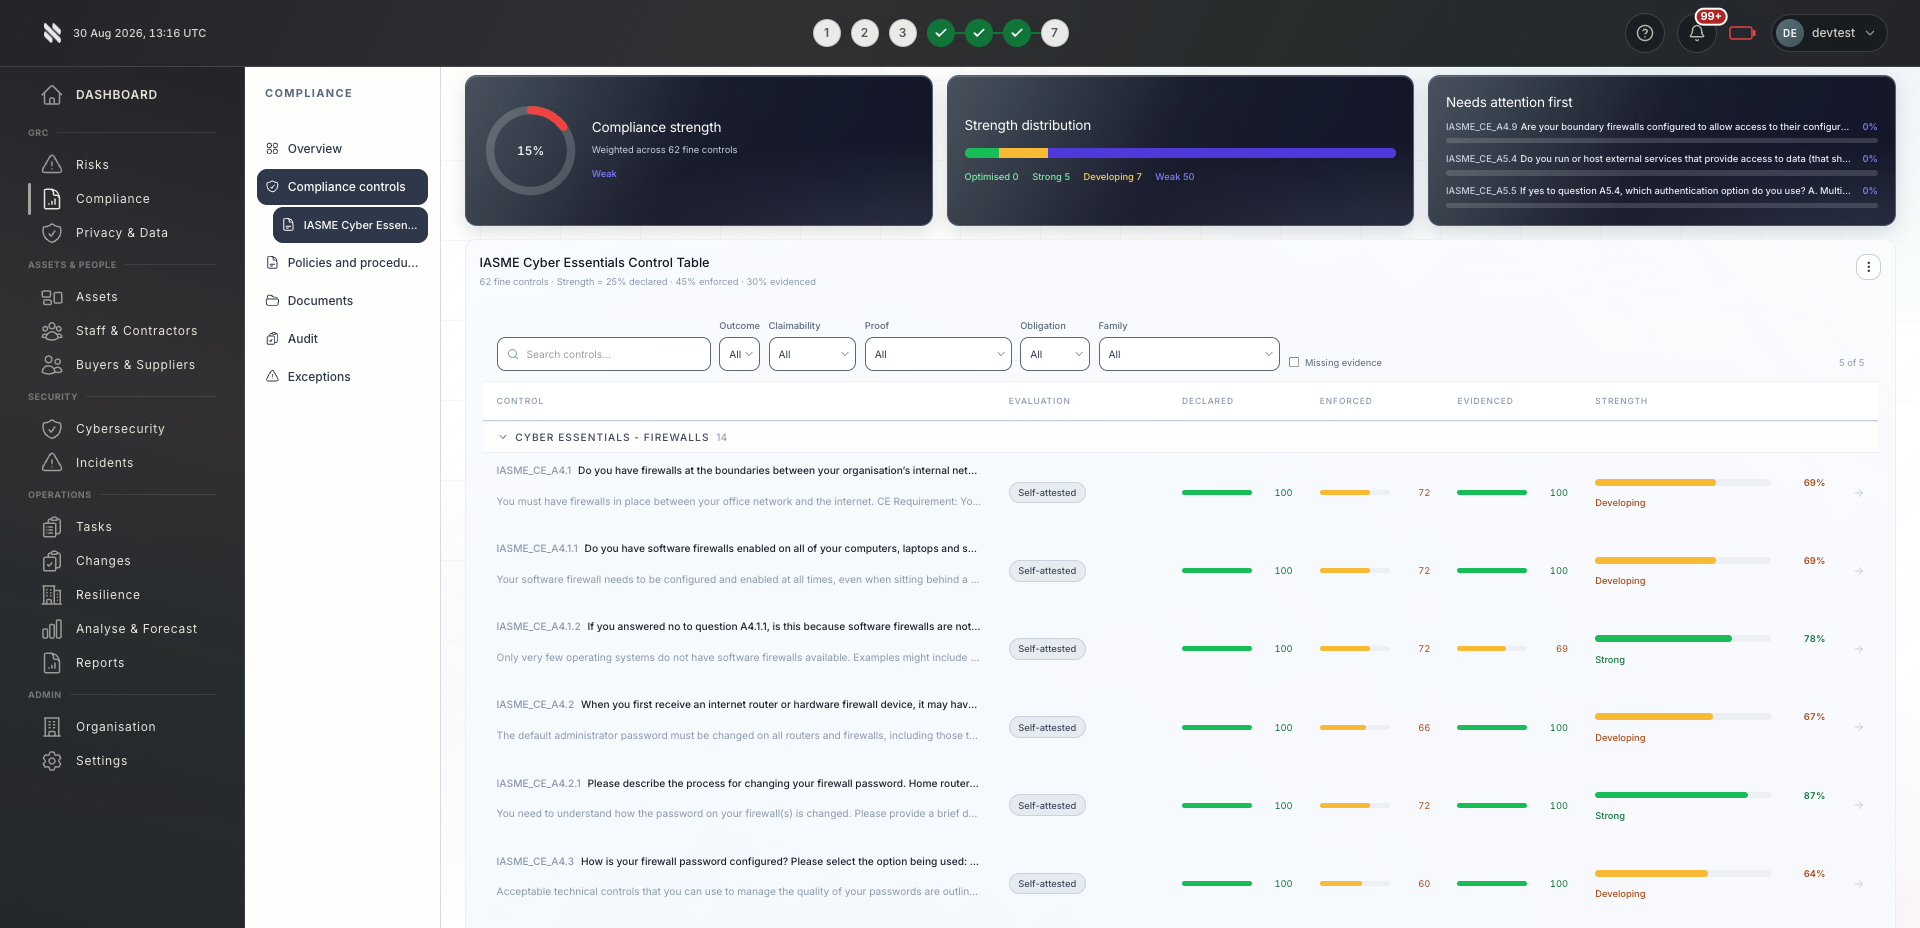
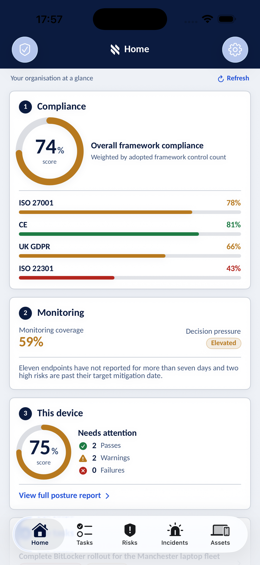
Bring delivery, oversight and assurance together without losing sight of who owns the next action.
Deliver ISO 9001 and ISO 27001 certification support as a combined service. Shared audit infrastructure reduces delivery cost per client.
Explore Fig for MSPs
Organisations pursuing dual certification (ISO 9001 + ISO 27001) no longer need two separate platforms. One system, one audit engine, one evidence library.
Explore Fig for organisationsShared evidence management across quality and security audits. CAPA tracking, management review records, and process metrics all available in one audit-ready system.
Discuss your requirementsStart with the outcomes you need. We will discuss scope, delivery and commercial terms with you before you commit.
Discuss your current approach to quality management, the teams involved and the requirements you need to meet.
See the relevant features in a tailored demonstration. Confirm integration coverage, responsibilities and any configuration needed.
Review the proposed scope and pricing. Set implementation priorities, ownership and review points around your organisation or client portfolio.
Platform functionality and automation depend on the agreed scope, configuration and connected systems. Software supports your compliance programme; it does not replace an independent assessment or guarantee certification.
Need to discuss a specific requirement or client scenario?
Speak to FigYes. Fig Group provides both QMS and ISMS capabilities with shared audit infrastructure, shared evidence management, and a single Control Evaluation Engine assessing both quality and security controls. This eliminates duplicate effort for dual-certification organisations.
CAPAs are raised from audit findings, incidents, or manual entry. Each CAPA follows a structured workflow: root cause analysis, corrective action definition, implementation tracking, effectiveness review, and closure verification. All linked to the originating finding.
Yes. Fig Group maps to all ISO 9001:2015 clauses including context of the organisation, leadership, planning, support, operation, performance evaluation, and improvement. Clause applicability is configurable per organisation.
Yes. QMS metrics and KPI tracking is built in, feeding into management review inputs. Process performance, customer satisfaction indicators, and quality objectives are all tracked with trend analysis.
Yes. The same audit infrastructure handles both quality and security audits. Audit planning, evidence curation, finding management, and remediation tracking work identically across both management systems.
Tell us what you would like to achieve. We will arrange a relevant conversation about the platform, your requirements and the right next step.
Continue exploring the prove capabilities, or return to the full platform overview.