Public Intake
Rate-limited API endpoint accepting anonymous vulnerability reports. Supports email, web form, API, and bug bounty platform channels. Reports routed to the right organisation automatically.
Public intake, approved disclosure policy and governed vulnerability handling.
Security researchers report vulnerabilities by email. Reports get lost in inboxes. There is no safe harbour policy. Disclosure timelines are missed. The process has no governance and no audit trail.
Rate-limited API endpoint accepting anonymous vulnerability reports. Supports email, web form, API, and bug bounty platform channels. Reports routed to the right organisation automatically.
Configurable policy controls can document scope, channels, response targets and lifecycle decisions. The organisation must approve and publish its policy; software cannot grant legal immunity to researchers.
Track reports through intake, triage, remediation, verification, disclosure and closure, with recorded transitions and severity rationale. Confirm the configured state model during implementation.
Disclosure timeline tracking with advisory URL linking. Coordinated disclosure with researcher communication. Metrics: MTTA, MTTR, SLA breach rate, and disclosure compliance rate.
This compliance controls view shows the wider Fig environment. Ask us to demonstrate vulnerability disclosure against your own requirements.
A tailored walkthrough lets you review the relevant workflows, supported connections and reporting before deciding whether Fig is right for your team.
See it in a demo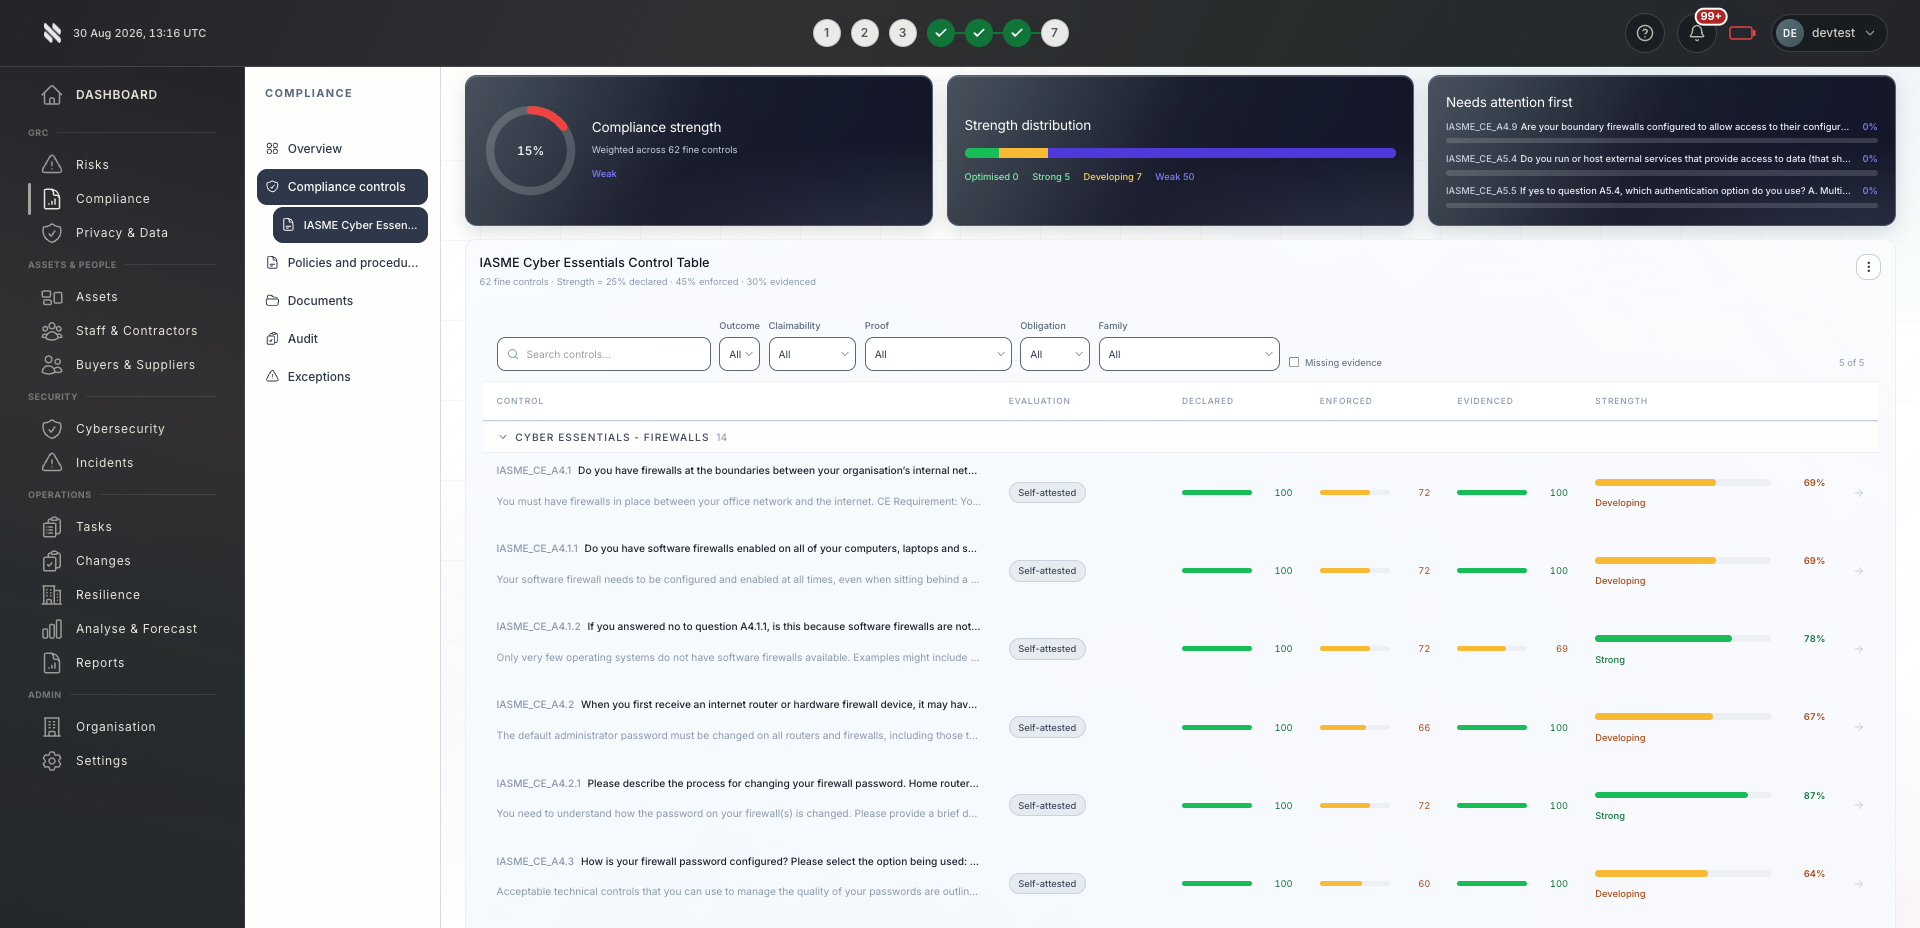
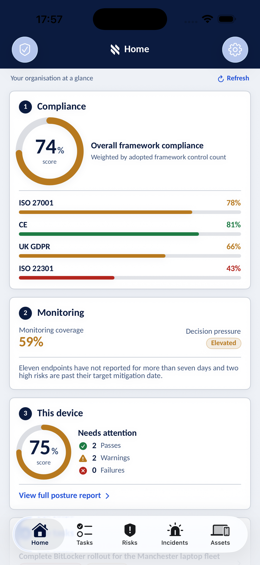
Bring delivery, oversight and assurance together without losing sight of who owns the next action.
Offer vulnerability disclosure programme management as a service. Standardised intake and governance across client portfolios.
Explore Fig for MSPs
Run a governed disclosure programme with records relevant to ISO/IEC 29147:2018 and ISO/IEC 30111:2019. Your approved policy and operating process determine actual conformity.
Explore Fig for organisationsComplete evidence of disclosure programme governance, researcher communications, remediation timelines, and lessons learned for regulatory review.
Discuss your requirementsStart with the outcomes you need. We will discuss scope, delivery and commercial terms with you before you commit.
Discuss your current approach to vulnerability disclosure, the teams involved and the requirements you need to meet.
See the relevant features in a tailored demonstration. Confirm integration coverage, responsibilities and any configuration needed.
Review the proposed scope and pricing. Set implementation priorities, ownership and review points around your organisation or client portfolio.
Platform functionality and automation depend on the agreed scope, configuration and connected systems. Software supports your compliance programme; it does not replace an independent assessment or guarantee certification.
Need to discuss a specific requirement or client scenario?
Speak to FigFor a basic disclosure programme, compare your intake, researcher communication and governance needs. Fig Group supports those workflows; bounty programmes involving rewards or a researcher community may need additional services.
A rate-limited endpoint (5 requests per IP per hour) accepts anonymous reports and routes them to the correct organisation. Researchers do not need an account. Reports include severity, description, and supporting evidence.
A published, approved policy should state testing scope, acceptable methods and how good-faith reports are handled. Fig Group can record policy decisions and flag exceptions, but legal protections depend on the policy and applicable law.
Yes. Disclosure reports can link to vulnerability remediation and verification records. Confirm how the configured disclosure states map to scanner finding states before relying on a shared workflow.
The workflow can help organise records relevant to ISO/IEC 29147:2018 disclosure and ISO/IEC 30111:2019 handling. Conformity depends on the organisation’s approved policy, communications and actual handling practice.
Tell us what you would like to achieve. We will arrange a relevant conversation about the platform, your requirements and the right next step.
Continue exploring the respond capabilities, or return to the full platform overview.